Quick summary
The U.S. Securities and Exchange Commission purchased warrantless access to a commercial airline database holding over one billion records — including passenger names, credit card numbers, flight details, and real-time booking alerts — operated by the Airlines Reporting Corporation (ARC). Documents obtained by 404 Media via FOIA request confirm the SEC, a civil financial regulator with no counterterrorism mandate, subscribed to ARC’s Travel Intelligence Program (TIP) and received daily notifications whenever tracked individuals booked new flights. Any traveler whose ticket passed through an ARC-connected agency is potentially in that dataset.
The program covered tickets from more than 270 airlines and thousands of agencies worldwide, including routes entirely outside the United States. ARC shut TIP down in November 2025 after media and congressional pressure — but the records it collected remain.
A civil financial watchdog built to police insider trading and securities fraud spent years quietly monitoring global flight bookings — no warrant, no court order, no public disclosure. Documents released under the Freedom of Information Act and first reported by 404 Media show the SEC subscribed to ARC’s Travel Intelligence Program, a commercial database that aggregated ticket settlements from accredited travel agencies and third-party booking platforms across more than 270 carriers worldwide.
The exposure is not theoretical. Passenger records in TIP included names, credit card numbers used at purchase, departure and arrival cities, flight numbers, and the agency that issued the ticket. The SEC’s subscription went further: it included automated daily alerts flagging any new bookings made in the previous 24 hours by individuals the agency was watching — effectively a prospective travel surveillance list, updated every morning.
For Western travelers flying to or through Asia-Pacific, the implications are direct. Tickets booked via U.S.-linked online travel agencies or corporate travel managers — even for itineraries with no U.S. airport in the routing — could have entered this database. Tokyo, Singapore, Sydney, Hong Kong: if a U.S.-accredited agency touched the transaction, the record was potentially there.
The SEC declined to comment on the program.
What ARC’s database actually contained — and who else was buying it
ARC is not a government body. It is an airline-owned financial clearinghouse — co-owned by American Airlines, Delta, and United — that settles ticket transactions between agencies and carriers. TIP was a commercial product built on top of that settlement infrastructure, and the SEC was not its only government customer.
Separate reporting confirms ARC’s travel intelligence products were marketed to and used by Customs and Border Protection, Immigration and Customs Enforcement, the FBI, and the Secret Service. The same commercial pipeline that fed a financial regulator’s watchlist also supported agencies with direct law enforcement and border control powers. The SEC’s use stands out precisely because it has neither — its mandate is civil, not criminal, and it carries no national security authority.
One structural detail matters for understanding the database’s reach: TIP captured tickets settled through intermediaries, not direct purchases. A traveler who books a flight on Japan Airlines‘ own website is unlikely to appear. A traveler who books the same flight through Expedia, a corporate travel manager, or a traditional travel agent almost certainly would — because those transactions route through ARC’s settlement system.
| Data element | Scope | Confirmed government users |
|---|---|---|
| Passenger name | Global — domestic U.S., international, and foreign-to-foreign routes | SEC, CBP, ICE, FBI, Secret Service |
| Credit card number used at purchase | Any ticket settled via ARC-accredited agency or platform | SEC confirmed via FOIA documents |
| Departure and arrival cities, flight dates and numbers | 270+ participating carriers worldwide | SEC confirmed via FOIA documents |
| Booking agency identity | Thousands of accredited travel agencies and OTAs | SEC confirmed via FOIA documents |
| Real-time booking alerts (24-hour lookback) | Prospective monitoring of named individuals | SEC (requested 1–25 daily alerts) |
404 Media‘s original reporting on the SEC’s ARC subscription remains the primary document source for this story. Additional detail on the database’s scale appears in coverage confirming the billion-record figure and the program’s multi-agency reach.
For travelers on flights from North America to Japan or elsewhere in Asia-Pacific, the practical question is whether their booking channel — not their airline — determined their exposure.
Flight deals
most people never see
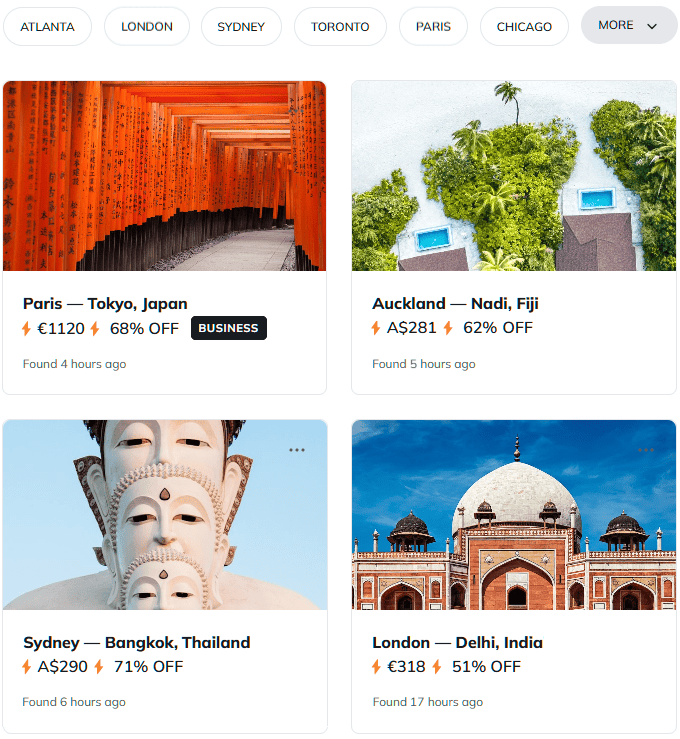
Our AI monitors 150+ airlines for pricing anomalies that traditional search engines miss. Air Traveler Club members save $650 per trip per person on average: see how it works.
Each deal saves 40–80% vs. regular fares:
Why a financial regulator could do this — and what the legal gap looks like
The mechanism here is the U.S. third-party doctrine: when you share information with a company, the Fourth Amendment’s warrant requirement generally does not follow that data. The government can buy it commercially instead. That is not a loophole someone discovered recently — it is a deliberate feature of how U.S. courts have interpreted privacy law for decades, and it applies to travel records as readily as it applies to phone metadata or financial transactions.
The contrast with other legal regimes is significant. Under the EU’s GDPR, data brokers face strict requirements around legal basis and purpose limitation — government agencies cannot simply purchase passenger records for investigative use without clearing higher legal bars. Australia and Singapore impose their own consent and purpose-limitation frameworks on commercial data flows, though neither is as comprehensive as GDPR in practice. A traveler whose itinerary is processed under U.S. legal infrastructure faces materially weaker protections than one whose booking stays entirely within European or Singapore-regulated systems — even when both are flying the same route.
Congress has not yet closed the gap. The proposed Fourth Amendment Is Not For Sale Act would bar agencies from purchasing data that would otherwise require a warrant, directly targeting the commercial data broker channel that TIP exploited. As of publication, the bill has not passed.
Steps to reduce your exposure on Asia-Pacific bookings
TIP is shut down, but the legal framework that enabled it remains intact — and other commercial travel data products built on similar infrastructure almost certainly still exist.
- Book directly on airline websites for Asia-Pacific itineraries. Tickets settled through ARC’s clearinghouse required an intermediary in the transaction chain. Purchasing directly on Singapore Airlines, Cathay Pacific, ANA, Japan Airlines, or other non-U.S. carriers’ own sites removes that intermediary for straightforward routes.
- Understand that corporate travel platforms carry risk. Many corporate travel management systems route settlements through ARC regardless of the carrier. If your employer books travel through a U.S.-accredited corporate travel manager, your itinerary data may still enter ARC-connected systems even on non-U.S. airlines.
- Treat OTAs as ARC-adjacent by default. Major online travel agencies — Expedia, Orbitz, Travelport-connected platforms — process transactions through ARC’s settlement infrastructure. Convenience comes with a data footprint.
- Review the Fourth Amendment Is Not For Sale Act. If you are a U.S. citizen or resident, this proposed legislation directly addresses the commercial data loophole. The U.S. House legislative database tracks its current status. Contacting your congressional representative is the one action that affects the structural problem rather than just your individual exposure.
- Assume historical records persist. ARC ended TIP in November 2025. The records it collected before that date were not deleted — they remain with the agencies that purchased access. Past itineraries are already in those systems.
Watch: Whether the Fourth Amendment Is Not For Sale Act advances in the current congressional session will determine whether the commercial data broker channel for travel records gets any statutory constraint. If it stalls again, expect similar programs to re-emerge under different product names — the commercial incentive for selling this data has not disappeared.
Questions? Answers.
Does ARC’s Travel Intelligence Program still operate?
No. ARC shut down TIP in November 2025 following sustained media coverage and questions from U.S. lawmakers about the program’s government data sales. However, records collected before that date remain with the agencies that purchased access, and the legal framework permitting warrantless commercial data purchases is unchanged.
If I booked directly on an airline’s website, was my data in the ARC database?
Probably not for that specific booking. TIP captured tickets settled through ARC-accredited travel agencies and third-party booking platforms — not direct purchases on airline websites. Travelers who booked directly on non-U.S. carrier sites were less likely to appear in the dataset, though codeshare and interline ticketing can complicate this.
Was the SEC the only government agency using ARC’s travel data?
No. ARC’s travel intelligence products were also marketed to and used by Customs and Border Protection, Immigration and Customs Enforcement, the FBI, and the Secret Service. The SEC’s use attracted particular attention because it is a civil financial regulator with no law enforcement or national security mandate.
Does this affect travelers who are not U.S. citizens?
Yes. The database covered global itineraries — including routes between foreign countries with no U.S. airport involved — whenever the ticket was issued through an ARC-participating agency. Citizenship is irrelevant; the booking channel determines exposure.
What data specifically was included in each passenger record?
According to documents obtained by 404 Media, records included passenger names, credit card numbers used for purchase, departure and arrival cities, flight dates and numbers, and the identity of the travel agency that issued the ticket.